AAA API Exposure Function
AAA-AEF is a session termination and rating engine that converges three different signalling protocols — CAMEL (CAP v1/v2 over SS7), RADIUS and Diameter — onto a single rating interface toward the OCS/CHF. Whether a session originates as a CAMEL IDP from a gsmSCF, a RADIUS Access-Request from a NAS, or a Diameter credit-control request from a PGW, AAA-AEF terminates it, requests a rating decision from the OCS in a common format, and applies the result — credit depletion, no-quota, mid-call failure — consistently regardless of which protocol carried the session.
Features & Benefits
Three session protocols, one rating path
CAP v1/v2, RADIUS and Diameter credit-control sessions all resolve to the same outbound rating request toward the OCS/CHF, aligned with the 3GPP charging data model — so quota and session outcomes look the same to the OCS no matter which network element originated the session.
Consistent quota handling across every protocol
No-quota and credit-depletion detection, and mid-call failure handling, are implemented identically across CAMEL, RADIUS and Diameter sessions — not three separate quota engines with three different behaviors.
MSRN-aware mobile-terminated handling
Mobile-terminated call scenarios that require MSRN allocation are handled as a dedicated code path in the RADIUS session logic, not bolted on as a special case.
Spending limit and AKA authentication, published through the operator's API framework
Beyond session termination, AAA-AEF exposes spending-limit notifications and AKA authentication challenge APIs, and publishes them to the CAPIF Core Function — so a subscriber's real-time spending status or authentication vectors can be exposed to an authorized application under the same onboarding and authorization framework as the rest of the exposure function family.
Converge CAMEL, RADIUS and Diameter onto one rating path
Session termination and rating, entirely inside the operator domain
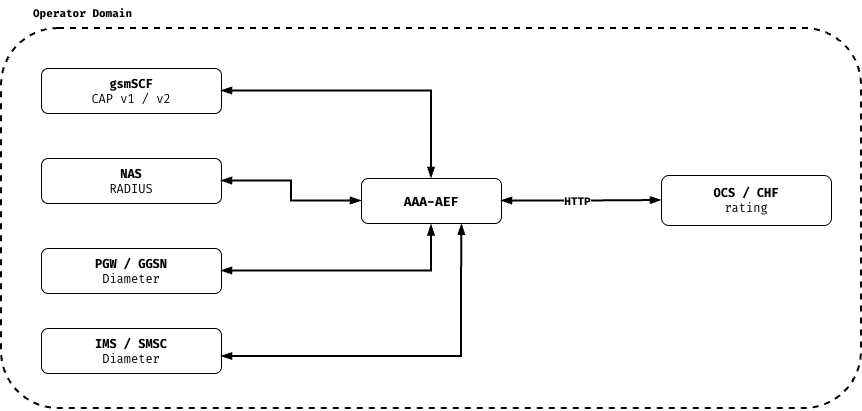
Deployed between session-originating network elements — a gsmSCF triggering CAMEL, a NAS sending RADIUS, a PGW sending Diameter credit-control — and the operator's own OCS/CHF, AAA-AEF terminates each session, converts it to a rating request and applies the outcome, independent of which protocol the session arrived on.
Credit depletion, no-quota and mid-call failure are handled the same way regardless of which protocol carried the session.
Expose spending limit and AKA APIs to a 3rd party domain with the CAPIF CF
AAA-AEF CAPIF mode, spending-limit and AKA-challenge APIs with 3rd Party Exposure
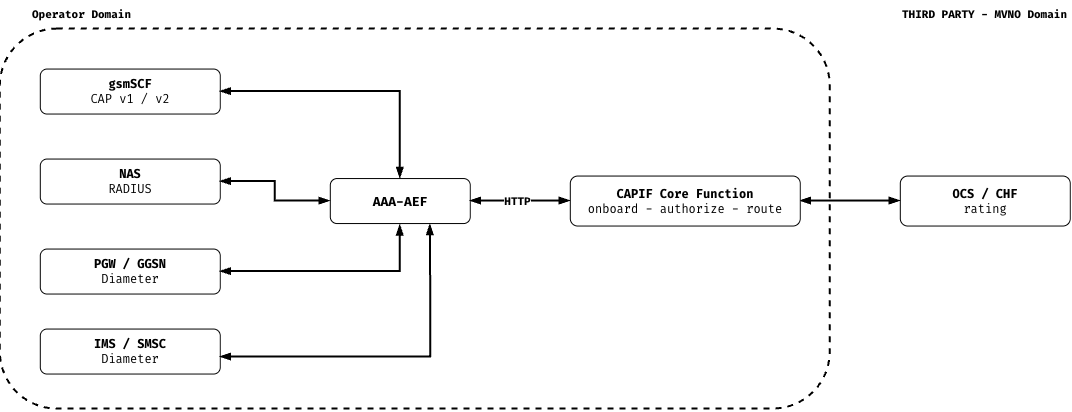
Where an operator exposes spending-limit notifications or AKA authentication challenges to an enterprise application, AAA-AEF publishes those service APIs to the CAPIF Core Function, which onboards the API invoker, applies the negotiated security method and routes authorized requests to the exposure function — while session termination and rating continue to run entirely inside the operator domain.
Technical specifications
Spending Limit Control
3GPP TS 32.294 style (Nchf-aligned)
AKA Authentication
3GPP TS 33.401 / 29.503 style
Admin / Session Control
Slicce internal (REST)
CAPIF
3GPP TS 29.222
CAP v1/v2 (CAMEL)
gsmSCF/gsmSSF, over TCAP/SCCP/M3UA/SCTP
ETSI/3GPP CAMEL Phase 1/2
TCAP / SCCP
ITU-T Q.771–Q.775 / Q.711–Q.714
M3UA / SCTP
IETF RFC 4666 / RFC 4960
RADIUS
Access, Accounting — NAS
IETF RFC 2865 / RFC 2866
Diameter Credit Control
PGW/GGSN
IETF RFC 4006
Rating Request
Outbound to OCS/CHF
3GPP TS 32.296 / 32.290 / 32.291 style
Architecture
3GPP TS 32.240 series charging data model (no single dedicated architecture document)
Ask us for the swagger file...
Contact us